CASINO
The MGM Hack’s Help Desk Bill Came Due Later
MGM’s 2023 help-desk hack cut about $100 million from quarterly profit, then a $45 million guest settlement and prison terms closed the first chapter.

MGM Resorts paid $45 million to settle customer suits over a 2023 casino hack that had already cut about $100 million from quarterly profit. The outage hit Bellagio, Aria, and Mandalay Bay, among other properties, after attackers talked a help desk into resetting access. Slot machines, room keys, and booking tools failed for days. Guests stood in analog lines on a Strip built for speed.
The company never paid the ransom. Rival Caesars Entertainment did, then watched investigators freeze most of the coins. By 2026, English-speaking members of the Scattered Spider cluster were drawing prison terms, and federal advice still opened with the same phone call.
Slot Machines Went Dark After One Phone Call
MGM told investors on September 12, 2023, that it had found a cybersecurity issue in certain U.S. systems and had shut them down to keep criminals off customer bank and card data. Public accounts of the intrusion, including a write-up circulated by the ALPHV/BlackCat ransomware brand used in the job, describe a LinkedIn lookup of an MGM staffer, then a short help-desk call that reset a password and multifactor login. Later technical write-ups put that login in Okta and say the callers enrolled a device they controlled. MGM’s own filing does not name the vendor or the length of the call.
Wendi Whitmore, then a senior vice president at Palo Alto Networks, described the usual script as a traveler who needed a reset.
They typically try to get a password reset by calling the help desk: “I’ve been traveling, I’ve just come back from vacation.”
Wendi Whitmore, senior vice president, Palo Alto Networks
Once inside, the crew moved through identity tools into the systems that run hotels and casino floors. ALPHV/BlackCat ransomware then locked virtual servers. A representative for Scattered Spider said the group took six terabytes from MGM and Caesars. MGM later said the actors got personal data on some customers who had done business before March 2019, and that it had no evidence the haul had been used for identity theft.
THE WEEK THE STRIP WENT ANALOG
- August 18, 2023: Attackers hit an outsourced IT vendor used by Caesars and begin moving toward the loyalty database.
- September 7, 2023: Caesars determines that a copy of its loyalty program database has been taken, including driver’s license numbers and Social Security numbers for a large share of members.
- September 12, 2023: MGM issues its public statement and says it shut systems after detecting the issue.
- September 14, 2023: Caesars files with the SEC; Scattered Spider claims six terabytes from both casino companies.
- October 5, 2023: MGM files its current report putting the September hit at about $100 million of strip and regional profit.
- November 16, 2023: The FBI and CISA publish their first joint warning on the group’s help-desk methods.
Charles Carmakal of Mandiant called the cluster among the most prolific threats to U.S. companies in that period. Native English let the callers sound like colleagues, not like a distant ransomware shop reading a script.
What the MGM Hack Cost the Company
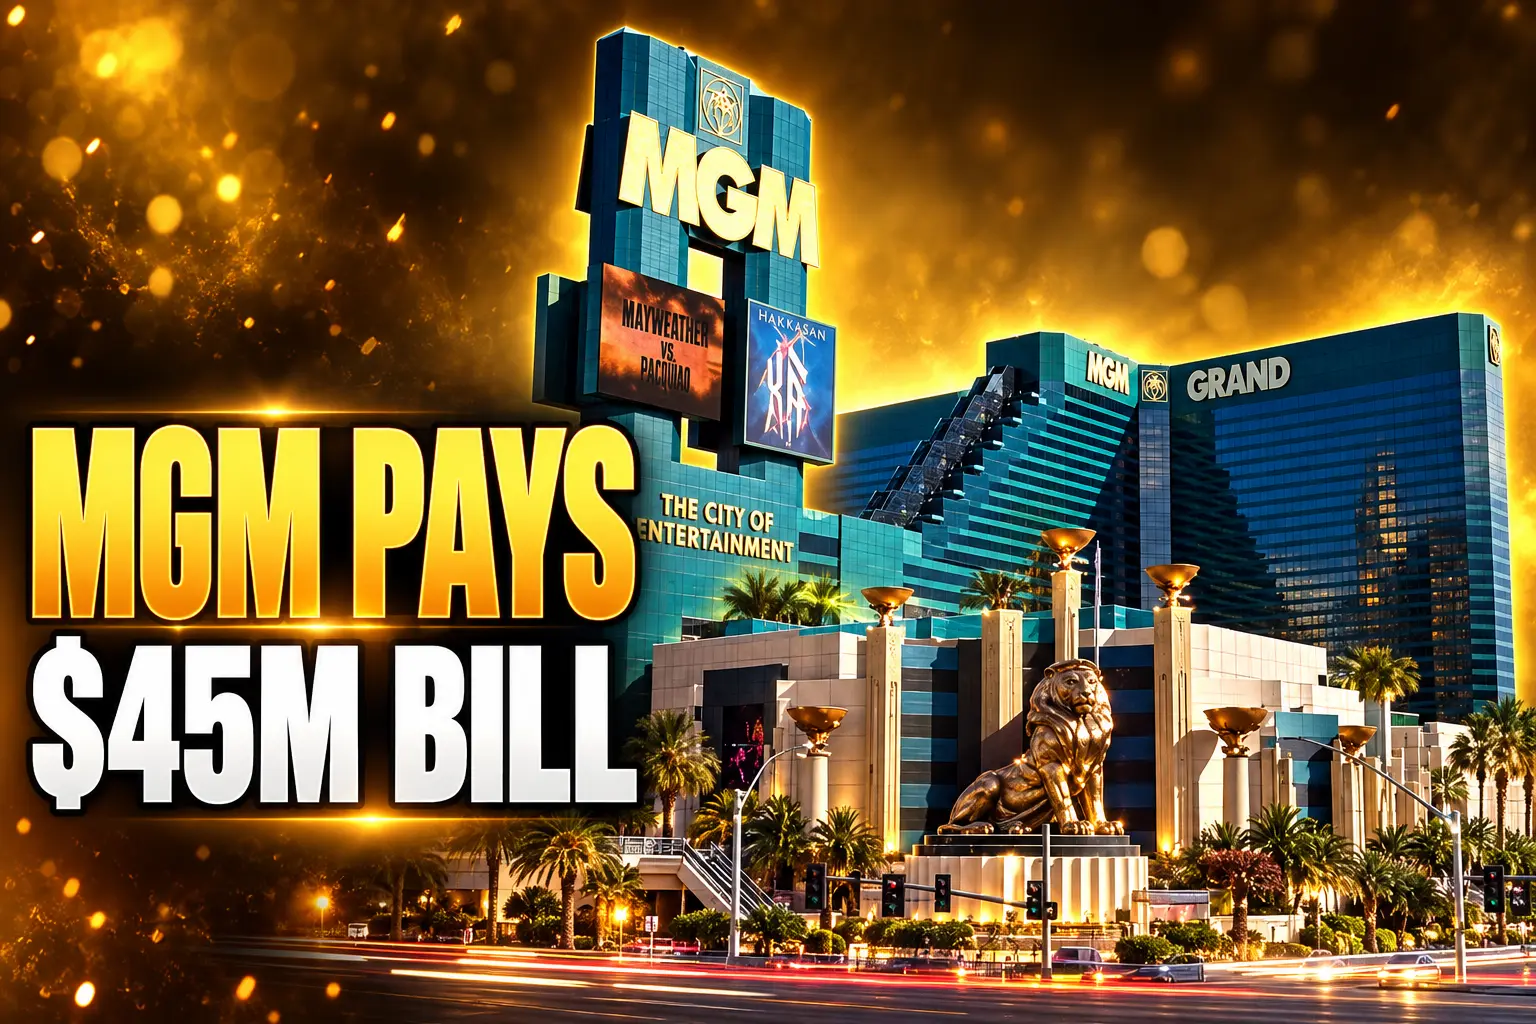
MGM’s October 5, 2023 current report is the clean accounting of the outage. It estimates a negative impact of about $100 million to quarterly profit, measured as Adjusted Property EBITDAR for Las Vegas Strip Resorts and Regional Operations together. It also booked less than $10 million of one-time costs for technology consultants, lawyers, and other advisers.
September occupancy at the Strip resorts was 88 percent, against 93 percent a year earlier. Management forecast 93 percent in October, against 94 percent the prior year, and said it expected a full rebound in November around Formula 1. It did not expect a material hit to full-year results. It also said it believed cyber insurance would cover the operating loss, the one-time bills, and later costs, while warning that the full scope was still open.
TWO STRIP COMPANIES, TWO BILLS
| Item | MGM Resorts | Caesars Entertainment |
|---|---|---|
| Public filing | October 5, 2023 (issue disclosed September 12) | September 14, 2023 (found September 7) |
| How they got in | Help-desk reset, per later technical accounts | Social engineering of an outsourced IT vendor |
| Ransom | Not paid | About $15 million, from a $30 million demand |
| Business hit | About $100 million of strip and regional profit, plus less than $10 million in one-time costs | No disruption of properties or mobile gaming disclosed |
| Customer data named | Pre-March 2019 contact files; a limited set of Social Security and passport numbers | Loyalty database with driver’s licenses and/or Social Security numbers |
| Money after the fact | $45 million class settlement covering 2019 and 2023 | Investigators later froze about 277.56 bitcoin from the ransom trail |
The $45 million guest fund is a separate check, and it also covers a 2019 incident. It is not a second count of the $100 million operating hit.
Caesars Paid and the FBI Froze Most of It
Caesars told the SEC the break-in was an outsourced IT support vendor attack. The filing says the actor copied the loyalty database, including driver’s license numbers and/or Social Security numbers for a significant number of members. Caesars said it had no evidence that passwords, bank accounts, or payment cards went with that copy. It offered credit monitoring to loyalty members and wrote that it had “taken steps to ensure that the stolen data is deleted by the unauthorized actor, although we cannot guarantee this result.”
Caesars never put a ransom figure in that filing. Chainalysis, working from an unsealed Nevada civil forfeiture case that matches the dates, describes a $30 million demand negotiated to about $15 million in cryptocurrency, with first access on August 18, 2023 and discovery on September 7. That is nearly three weeks inside the network before the company says it knew.
MGM chief executive Bill Hornbuckle later said his teams were already rebuilding when a ransom note arrived, so he did not answer it. He framed it as timing, not a speech about refusing criminals. The FBI’s public guidance still warns that paying does not guarantee a return of data and can invite the next attempt.
In January 2024, five months after that payment, investigators flagged about 402 bitcoin moving through Avalanche Bridge, then worth about $11.8 million. Ava Labs froze 277.56 bitcoin. A further transfer of about $690,000 in mixed coins went to Gate.io, which froze those funds in early February after an FBI request. Chainalysis documented that FBI freeze of 277 bitcoin as the core recovery on the Caesars trail. Paying still moved money to the crew. It did not keep the coins out of reach forever.
CISA’s Live Warning Still Starts With a Call
The FBI and CISA first published a joint advisory on Scattered Spider on November 16, 2023. They updated it on July 29, 2025 with partners in Canada, Australia, and the United Kingdom, using FBI work through June 2025. The first sentence of the technical story has not moved. Scattered Spider “targets large companies and their contracted information technology (IT) help desks.”
The 2025 update adds DragonForce ransomware to the older ALPHV/BlackCat pairing. It also states, in plain language, that callers now pose as employees to get help-desk staff to reset a password and move MFA onto a device the caller holds. That is the MGM pattern written as a standing method, not a one-off Vegas trick.
WHAT THE ADVISORY SAYS THEY STILL DO
- Help-desk resets: Callers pose as staff or contractors and talk a desk into a password and MFA reset on a device they control.
- MFA fatigue: Repeated push prompts until someone hits accept, then a new device is enrolled.
- SIM swaps: A mobile number is moved so one-time codes land with the attacker.
- Lookalike login pages: Domains built like a company help desk or Okta portal, even if that exact lure is not used every time.
- Living-off-the-land tools: Ordinary remote-access software such as AnyDesk, ScreenConnect, Ngrok, and Tailscale, which blend into help-desk traffic.
- Extortion after theft: Data copied first, then encryption, with talks over Tor, Tox, email, or encrypted chat.
The controls that match that list are dull on purpose. CISA’s first asks are offline backups stored away from production, phishing-resistant MFA, and rules that limit what software can run. Practitioners who still work this beat keep repeating a verified callback at the desk, hardware keys on privileged accounts, and a hard split between corporate identity and the hypervisors that run casino floors. Those are not new products. They are the doors the 2023 call walked through.
Through 2025 the same cluster was tied to British retailers, including Marks & Spencer, Co-op, and Harrods, and to Transport for London. The names on the victim list changed. The help desk did not.
Prison for Some, a Brand That Persists
Scattered Spider was never a single payroll. It is a loose English-speaking network, also tracked as UNC3944, Octo Tempest, Oktapus, and Muddled Libra, sitting inside a wider scene nicknamed The Com. That is why arrests have not retired the label.
On July 16, 2026, Woolwich Crown Court sentenced Owen Flowers, 18, and Thalha Jubair, 20, to 5 years and 6 months each for the 2024 Transport for London intrusion, which also began at a help desk. Both had changed their pleas to guilty on June 22, 2026. Brett Leatherman, assistant director of the FBI’s Cyber Division, called the result a step in holding two members to account. U.K. officers said the case slowed that cell. They also said other criminals still borrow the brand.
In the United States, Noah Michael Urban, 21, of Palm Coast, Florida, drew 10 years in federal prison and $13 million in restitution. Tyler Robert Buchanan, 24, of Dundee, Scotland, pleaded guilty on April 17, 2026, to conspiracy to commit wire fraud and aggravated identity theft in a Central District of California case that the Justice Department tied to at least $8 million in stolen cryptocurrency. He faces a statutory maximum of 22 years. A docket entry most recently listed his sentencing for September 29, 2026, after several delays. Court records in the same case show Evans Onyeaka Osiebo sentenced on August 14, 2026, to 45 months, and Joel Martin Evans sentenced on August 27, 2026, to 24 months. Co-defendant Ahmed Hossam Eldin Elbadawy pleaded not guilty in October 2025. Those counts cover a phishing and crypto-theft stretch that ends in April 2023, before the Strip casinos were hit, and the charging papers do not name MGM or Caesars as victims in that indictment.
A juvenile suspect tied by Las Vegas police to the casino intrusions surrendered at Clark County Juvenile Detention on September 17, 2025, on identity theft, extortion, and computer intrusion charges. The district attorney sought to move the case into adult court. In July 2026, the Justice Department said Peter Stokes, a 19-year-old dual U.S. and Estonian citizen known as Bouquet, had been extradited from Finland after an arrest at Helsinki Airport. Prosecutors allege he took part in more than 100 intrusions and more than $100 million in ransom payments. Those are charges, not findings.
The people in the dock are young. The method they used is old-fashioned enough to survive a new defendant list.
The $45 Million Check Arrived in December
On the customer side, the 2023 incident did not close with the 8-K. Consolidated suits over the July 2019 and September 2023 data incidents were resolved in Tonya Owens, et al. v. MGM Resorts International et al. in the U.S. District Court for the District of Nevada. MGM agreed to a $45 million fund. A judge granted final approval on June 18, 2025. The official $45 million customer settlement site says payments for approved cash claims went out on December 12, 2025.
Plaintiffs’ lawyers said the two incidents together touched more than 37 million customers. MGM has not published its own headcount. The 2023 filing said names, contact details, gender, dates of birth, and driver’s license numbers were taken for some pre-March 2019 customers, with Social Security and passport numbers for a limited set. It said passwords, bank accounts, and payment cards were not believed taken.
WHAT THE SETTLEMENT PAID
- Tier 1: An estimated $75 if a Social Security number or military ID was exposed.
- Tier 2: An estimated $50 if a passport or driver’s license number was exposed.
- Tier 3: An estimated $20 if name, address, and/or date of birth was exposed.
- Documented losses: Up to $15,000 with receipts, plus one year of financial account monitoring for eligible claimants.
The claim deadline was June 3, 2025. Monitoring enrollment mail went out from December 16, 2025. For a guest whose slot machine froze in September 2023, the cash arrived more than two years later, in amounts that look small next to the company’s $100 million operating line and small next to a $15 million ransom. They are the only dollars most of those guests will ever see from the incident.
MGM got the floors running again in time for Formula 1. Caesars kept the lights on by paying, then lost most of that pile when the coins were frozen. Insurers were told they would carry MGM’s operating hit. Help-desk vendors sat in the middle of both jobs and barely appear in the filings. The people who answered the phone that week are still the cheapest way into a casino network, which is why the federal advisory, two years after the first version, still starts there.
Frequently Asked Questions
Did MGM Pay a Ransom in the 2023 Casino Hack?
No. Chief executive Bill Hornbuckle said the ransom note arrived after MGM had already started rebuilding systems, and the company did not respond. The FBI’s public ransomware guidance warns that a payment does not guarantee data will be returned and can mark a firm as willing to pay. MGM’s October 5, 2023 filing is silent on any demand amount.
What Customer Data Did the MGM Hackers Take?
MGM said the actors obtained, for some customers who transacted before March 2019, names, phone numbers, email and postal addresses, gender, dates of birth, and driver’s license numbers, and that for a limited number they also obtained Social Security and passport numbers. The company said it did not believe passwords, bank account numbers, or payment card data were taken, and it said The Cosmopolitan of Las Vegas systems and data were not accessed. It set up a help line at 800-621-9437 and told callers to use engagement number B105892.
How Much Was the MGM Data Breach Settlement?
The court-approved fund is $45 million and covers both the July 2019 and September 2023 incidents in Owens, case number 2:23-cv-01480-GMN-NJK, in the District of Nevada. Eligible people could claim tiered cash of about $20, $50, or $75, or documented losses up to $15,000, plus a year of account monitoring. Claims closed June 3, 2025, and approved cash payments were sent December 12, 2025.
Did Caesars’ Las Vegas Properties Shut Down Like MGM’s?
Caesars said customer-facing operations, including physical properties and online and mobile gaming apps, were not disrupted. The harm it disclosed was a copied loyalty database, not dark slot floors. That difference is why a ransom near $15 million can look cheap next to MGM’s about $100 million operating hit, even before investigators froze most of the Caesars coins.
What Does CISA Tell Casinos to Change After Scattered Spider?
The July 29, 2025 advisory tells commercial facilities to keep offline backups that are stored apart from live systems and tested, to enforce phishing-resistant multifactor authentication, and to control which applications can run. It also flags contracted help desks as the opening target, which means a reset on a privileged account should require a callback or a second person, not a single convincing story about a lost phone.
Disclaimer: This article is news reporting and analysis of public filings, court records, and government advisories. It is for information only and is not legal advice, investment advice, or guidance on identity-theft claims or insurance coverage. Readers who think their data was involved, or who hold MGM or Caesars securities, should speak with a qualified attorney, a licensed financial adviser, or an identity-theft professional before filing a claim or making a money decision. Figures, case statuses, and settlement mechanics come from the public documents named in the piece and may change as courts and companies update them.

The Seminole Tribe’s $4 Billion Hard Rock Guitar Takes the Strip

Star Entertainment’s $1 Million Loss Leaves Sydney Exposed

Resorts World Turns a Compliance License Into an Arena Bid

William Latta Claims His First RGPS Tunica Ring

Caesars’ Las Vegas Strip Bet Now Runs Through Conventions

Revo’s Manchester Rebuild Outgrew Its First Approval

Bally’s Stayed Listed After the $4.6 Billion Takeover

Interior Hands Redding Rancheria the I-5 Casino Frontage

New Jersey Asked Miss America Home With No Money

Churchill Downs’ $100 Million Owensboro Bet Is Paying
-
 CASINO2 years ago
Revo’s Manchester Rebuild Outgrew Its First Approval
-
 CASINO2 years ago
Interior Hands Redding Rancheria the I-5 Casino Frontage
-
 CASINO2 years ago
Bally’s Stayed Listed After the $4.6 Billion Takeover
-
 CASINO2 years ago
Churchill Downs’ $100 Million Owensboro Bet Is Paying
-
 CASINO2 years ago
New Jersey Asked Miss America Home With No Money
-
 NEWS2 years ago
Dutch Courts Leave Pre-2021 Casino Losses With Operators
-

 CASINO2 years ago
Chickasaw Nation Opened OKANA Resort With No Casino
-
 CASINO12 months ago
Atlantic City’s 2025 Tourism Win Left a Thinner Resort